Google and Microsoft accounts
Link a mailbox, calendar and files in one click with Connect, or through your organization's own Google and Microsoft app.
On this page
- Where to find it
- Link an account in one click
- Link an account with your own choices
- Using your own app
- Microsoft
- Moving between your own app and one click
- When an account shows Reconnect
- Watching a linked mailbox for new mail
- Unlinking
- Managing and deleting your data
- Removing access at Google or Microsoft
- Common mistakes
- Next
Linking a Google or Microsoft account lets an agent work inside somebody's real mailbox: reading mail, sending replies, and for Google also reading a calendar, dropping a file in Drive or appending to a Sheet.
There are two ways to link, and most organizations only ever need the first.
- Connect, in one click. Press Connect, approve access on Google's or Microsoft's own screen, and the account is linked. There is nothing to register and nothing to paste.
- Your own app. An organization that wants its own name on the consent screen, or whose IT policy only allows apps it registered itself, adds its own Google or Microsoft app first. From then on Connect uses that app for everyone in the organization.
Where to find it
- Connections, in the sidebar. The Gmail, Google Calendar, Google Drive, Google Sheets and Outlook cards each have a plus. Anyone who builds in the project can use them.
- Connectors, which Open in Kareenos above opens, as does Manage connections, then Connectors and email, in Connections. Administrators only. It has the Google and Microsoft cards under Google & Microsoft, and the Linked Accounts list at the bottom.
Link an account in one click
- Choose the project in the top bar. Every linked account belongs to one project, and only agents in that project can use it.
- Press Connect on the Google or Microsoft card. In Connections, press the plus on the card for the service you want.
- A window opens on the provider's own sign in and consent screen. Choose the account and approve.
- The window closes on its own and the account appears under Linked Accounts.
One click links the account as private to you. From a Google or Microsoft card it asks for every service on offer; from a card in Connections it asks for that card's service only. A service that is not on offer is left out: its card in Connections says so, and your organization's own app is the way to link it. To decide these yourself, use Add Account below.
Important
On Google's screen you can untick individual permissions. Anything you untick is a service your agents will not have. Kareenos tells you which services were left out, and linking the same account again with every box ticked adds them.
Note
If Connect is greyed out, one click linking is not switched on for that provider on this platform yet. In Connections the plus then leads to the setup of your own app instead. Your organization can link through its own app in the meantime: see Using your own app below.
If your browser blocks the sign in window, Kareenos says so. Allow pop-ups for the site and press Connect again.
Link an account with your own choices
Press Add Account in the Linked Accounts section.
Choose the Project.
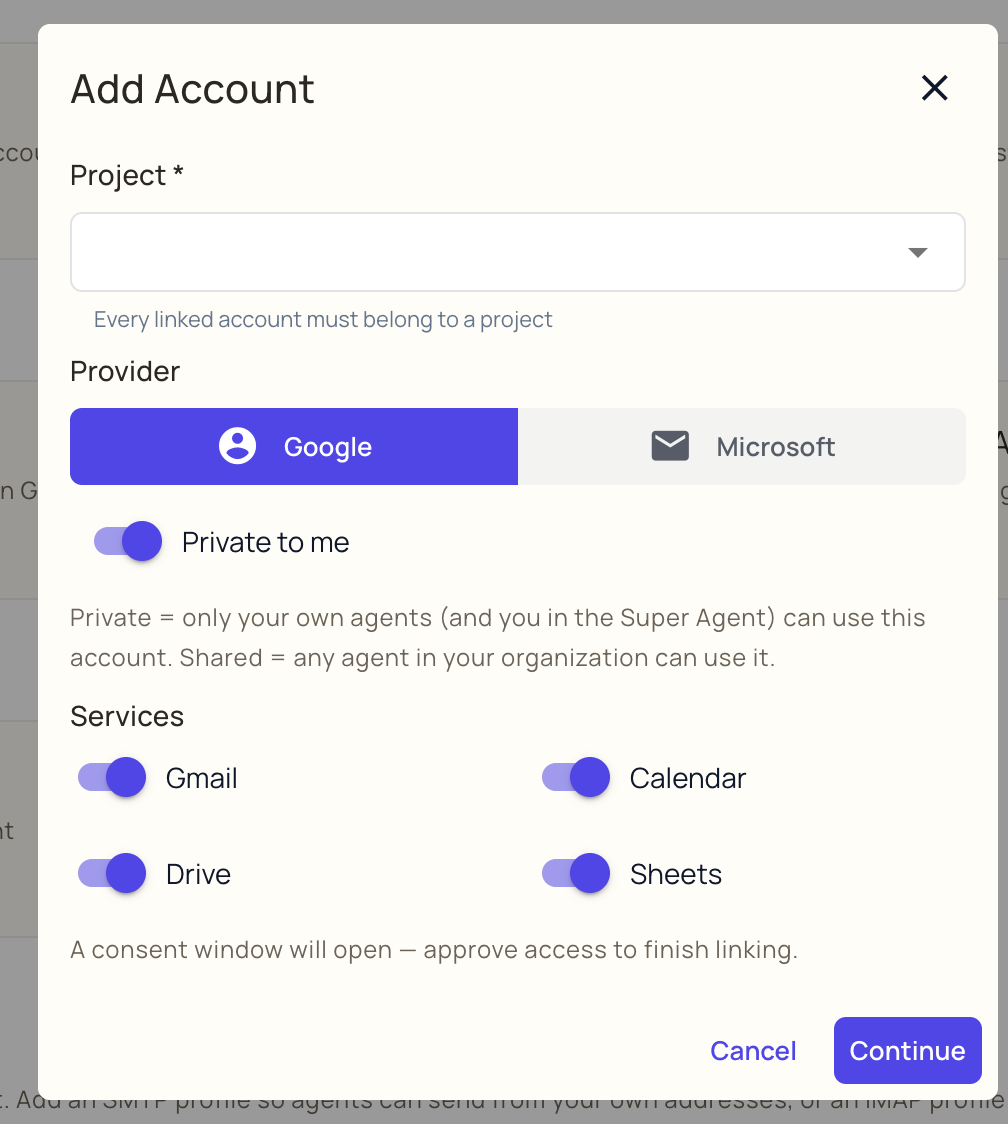
Choose Google or Microsoft. A greyed out provider cannot be linked yet, by one click or through your own app.
For Google, choose which services to allow. Turn off anything the agents do not need. Only the services that can be linked are listed. Gmail lets agents read, draft and send, and is offered when your organization uses its own Google app; with one click it is Gmail (send only), which lets them send and nothing else. For Microsoft, linking connects Outlook mail: reading and sending, plus drafts when your organization uses its own Microsoft app.
Decide Private to me or shared. Private means only your own agents, and you in the Super Agent, can use the account. Shared means any agent in your organization can. If the project itself is private, the link is forced to private too.
Press Continue, then approve on the provider's screen.
The link then appears in the list with the provider, the services it covers, whether it is private or shared, which app linked it and its project.
Using your own app
Your organization can register its own Google Cloud project or its own Microsoft app registration. The consent screen your people see then carries your name, and the access sits inside your own cloud account where your administrators can review or revoke it. It is a one time job for an administrator.
Once your own app is saved and Active, Connect uses it for everyone in your organization. Accounts linked before that keep working through the app that linked them.
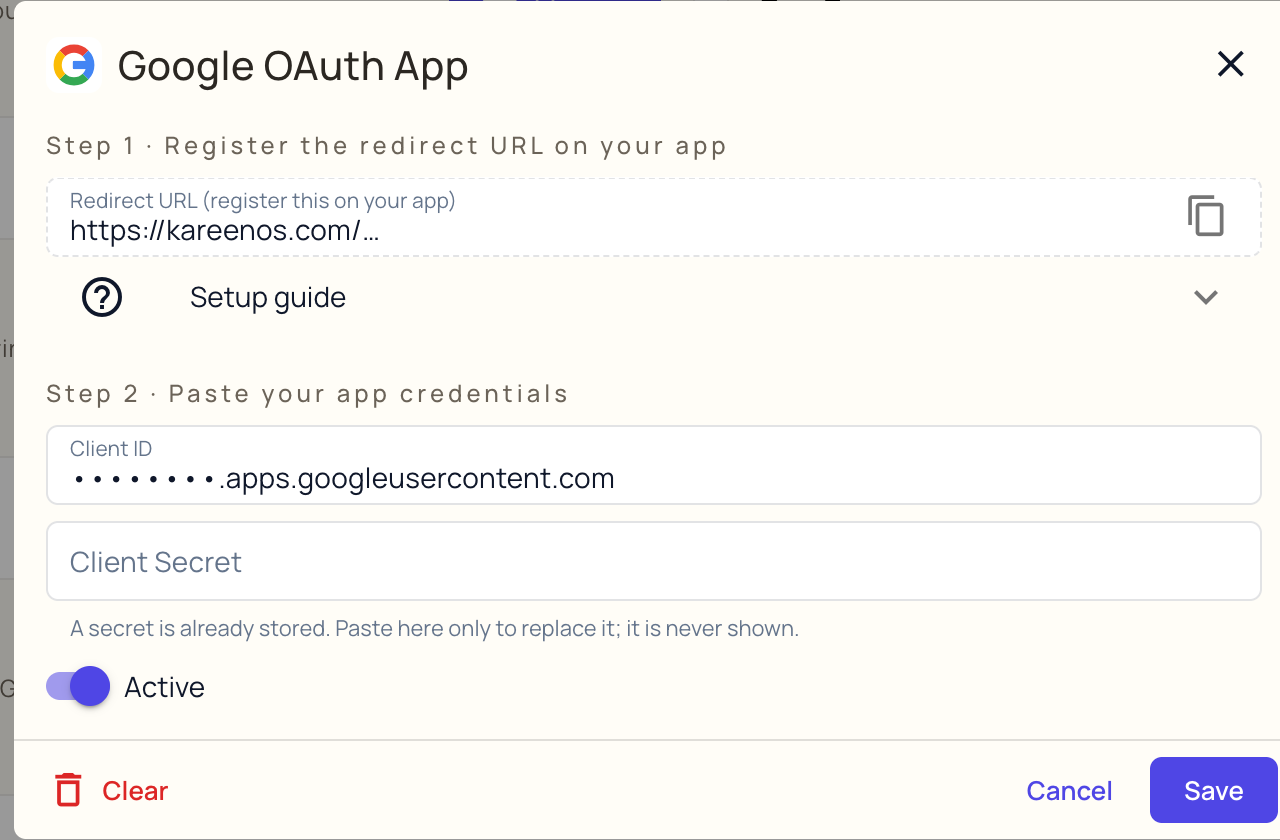
Open Connectors and press Use your own app on the Google card.
At the top of the dialog is a read only Redirect URL. Press the copy button beside it. Do not retype it. It has to match on both sides exactly, and a typed copy is the single most common reason linking fails later.
Open the Google Cloud console credentials page, in your own Google Cloud project.
Choose Create Credentials, then OAuth client ID, then application type Web application.
Paste the Redirect URL into Authorized redirect URIs.
Under APIs and Services, then Library, enable the services your agents will actually use: Gmail API, Google Calendar API, Google Drive API, Google Sheets API.
Configure the OAuth consent screen, choosing External.
Copy the Client ID and Client Secret back into the dialog, leave Active on, and press Save.
Important
While your consent screen is in Testing, only people you have explicitly added as test users can link an account, and their access expires after seven days. Everyone else is refused at Google's own screen, which looks like a Kareenos problem and is not. Either add each colleague as a test user, or publish the app and complete Google's verification.
Microsoft
Open Connectors and press Use your own app on the Microsoft card.
Copy the Redirect URL with the copy button, the same as above. The dialog's own Setup guide repeats the steps below.
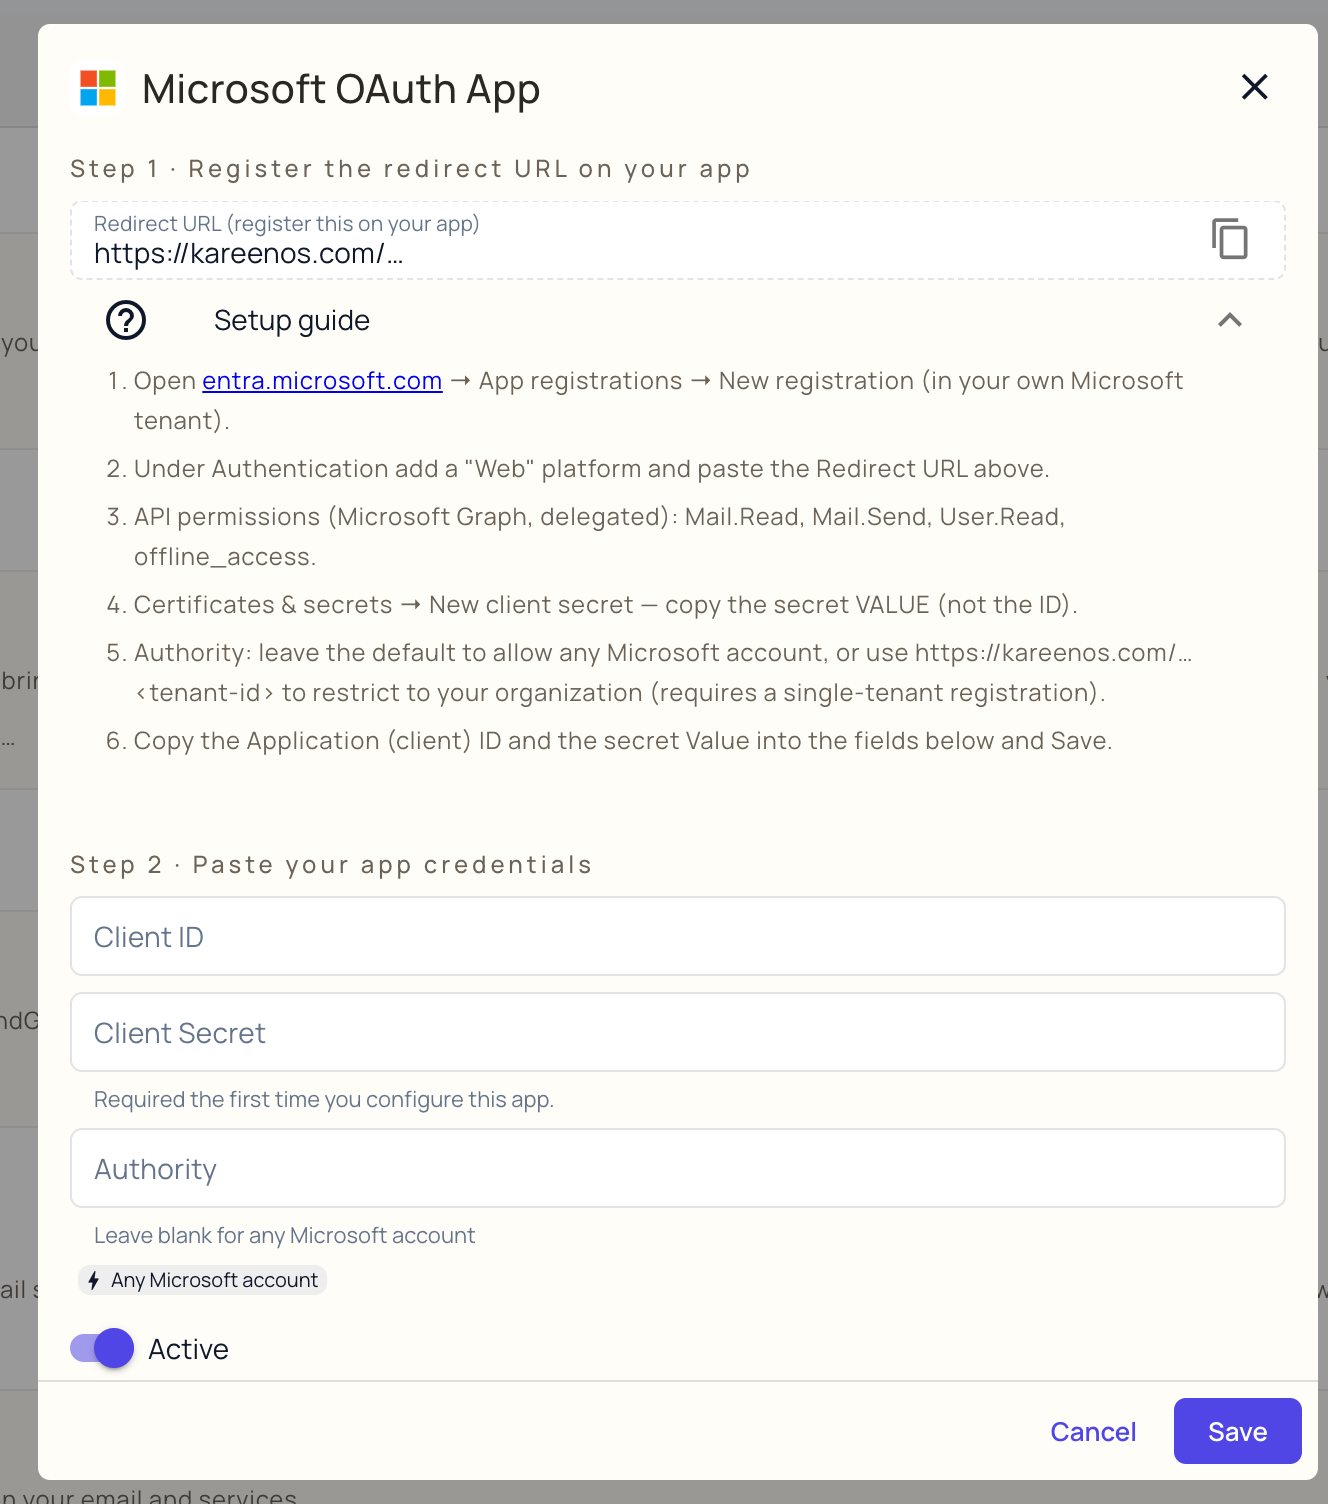
Open the Microsoft Entra admin center, go to App registrations and choose New registration, in your own Microsoft tenant.
Under Authentication, add a platform of type Web and paste the Redirect URL.
Under API permissions, add these delegated Microsoft Graph permissions: Mail.Read, Mail.Send, Mail.ReadWrite (for drafts), User.Read and offline_access.
Under Certificates and secrets, choose New client secret. Copy the secret Value, not the Secret ID. The Value is only shown once and the two are easy to confuse.
Back in the dialog, paste the Application (client) ID and the secret Value.
Leave Authority blank to allow any Microsoft account to link, or set it to your own tenant to restrict linking to your organization. Restricting it requires a single tenant registration.
Leave Active on and press Save.
Moving between your own app and one click
An account stays with the app that linked it. Changing which app Connect uses never moves an account by itself.
- To stop using your own app: open it with Use your own app, switch Active off and save. New links then go through one click. The accounts linked through your own app wait, and each shows Reconnect. Press it and approve once, and the account continues through one click.
- To start using your own app: set it up as above. New links use it at once. Accounts linked by one click keep working as they are; reconnect one only if you want it on your own app.
When an account shows Reconnect
Reconnect appears when an account cannot be used as it stands:
- Access was withdrawn or has expired at Google or Microsoft.
- The app the account was linked through is switched off. It resumes by itself when the app is switched back on.
- The account was linked through a different app than the one in use now.
Press Reconnect, approve on the provider's screen, and the same account is back in the same project.
Watching a linked mailbox for new mail
Each mail capable link has an Auto-sync email toggle and an interval in minutes. Switch it on and agents are woken when new mail arrives in that mailbox, the same way an IMAP profile works for a company mail server. Leave it off if you only want agents to read or send when asked.
Unlinking
Press the unlink button on the row. Agents immediately lose access to that account's services, and anything that depended on it starts reporting the account as unavailable. Linking it again is one click, so unlinking to test something is safe.
Nobody else can unlink your private account for you, and a shared link is worth agreeing on before removing, since other people's agents may be using it.
Managing and deleting your data
Kareenos does not keep a copy of a linked mailbox, calendar or files. They stay with Google or Microsoft.
- To stop access, unlink the account, as above. The stored access is deleted at once.
- To delete a conversation, open the menu beside the chat in the agent's chat list and choose Delete.
- To delete what an agent remembers, open Agent Memory, tick the entries and press Delete selected.
- To have your data deleted for you, write to
privacy@kareenos.ai.
Our Privacy Policy describes how this data is used.
Removing access at Google or Microsoft
Unlinking in Kareenos is enough to stop your agents. To also withdraw the permission at the provider:
- Google: open the linked apps page of your Google Account, select Access to your Google Account, choose the app, then See details, Remove access and Confirm.
- Microsoft, personal account: open the apps and services you have given access to, find the app and remove its permissions.
- Microsoft, work or school account: open My Apps, open the menu on the app, choose Manage your application, then Revoke permissions.
The app is listed as Kareenos when you linked in one click, and under your organization's own app name when you linked through your own app.
Common mistakes
- Unticking a permission on Google's screen, then wondering why the agent cannot read the calendar.
- Linking the same mailbox from a second project and expecting it in both. An account sits in one project; linking it from another moves it there.
- Linking a personal mailbox for a company function. When that person leaves, every agent that relied on it stops. For a shared company address, use an email profile instead.
- With your own app: typing the Redirect URL instead of copying it. It has to match character for character.
- With your own app: copying the Microsoft secret ID instead of the secret Value.
- With your own Google app: leaving the consent screen in Testing and forgetting to add colleagues as test users.